
What is a Wi-Fi captive portal?
A captive portal is a special web page that appears when newly connected users try to access a wireless network or internet access for the first time. You’ve probably seen one in coffee shops, airports, or business centers—before you can browse the web, you’re greeted by a portal page asking you to log in, register, or accept terms and conditions. This process is a key part of network security, as it ensures that only authorized users are granted broader access to the network.
Implementing captive portals allows network administrators to control who can connect to the network, protecting sensitive data and reducing the risk of unauthorized access. By requiring users to interact with a captive portal page, businesses can manage internet access, monitor usage, and maintain a secure environment for everyone. Whether you’re running a business center, managing a public hotspot, or providing guest Wi-Fi, captive portals are an essential tool for keeping your network safe and organized.
Captive portal security covers everything that protects guests, your network, and your organization when visitors connect to Wi-Fi through a login page. A captive portal controls who gets online, but on its own it does not encrypt traffic, isolate guests, or stop a fake portal. The 10 practices below close those gaps. They are written for IT and network teams running guest Wi-Fi across offices, hotels, retail stores, and campuses.
Ten best practices to secure your Wi-Fi captive portal
1. Isolate guest traffic from your corporate network
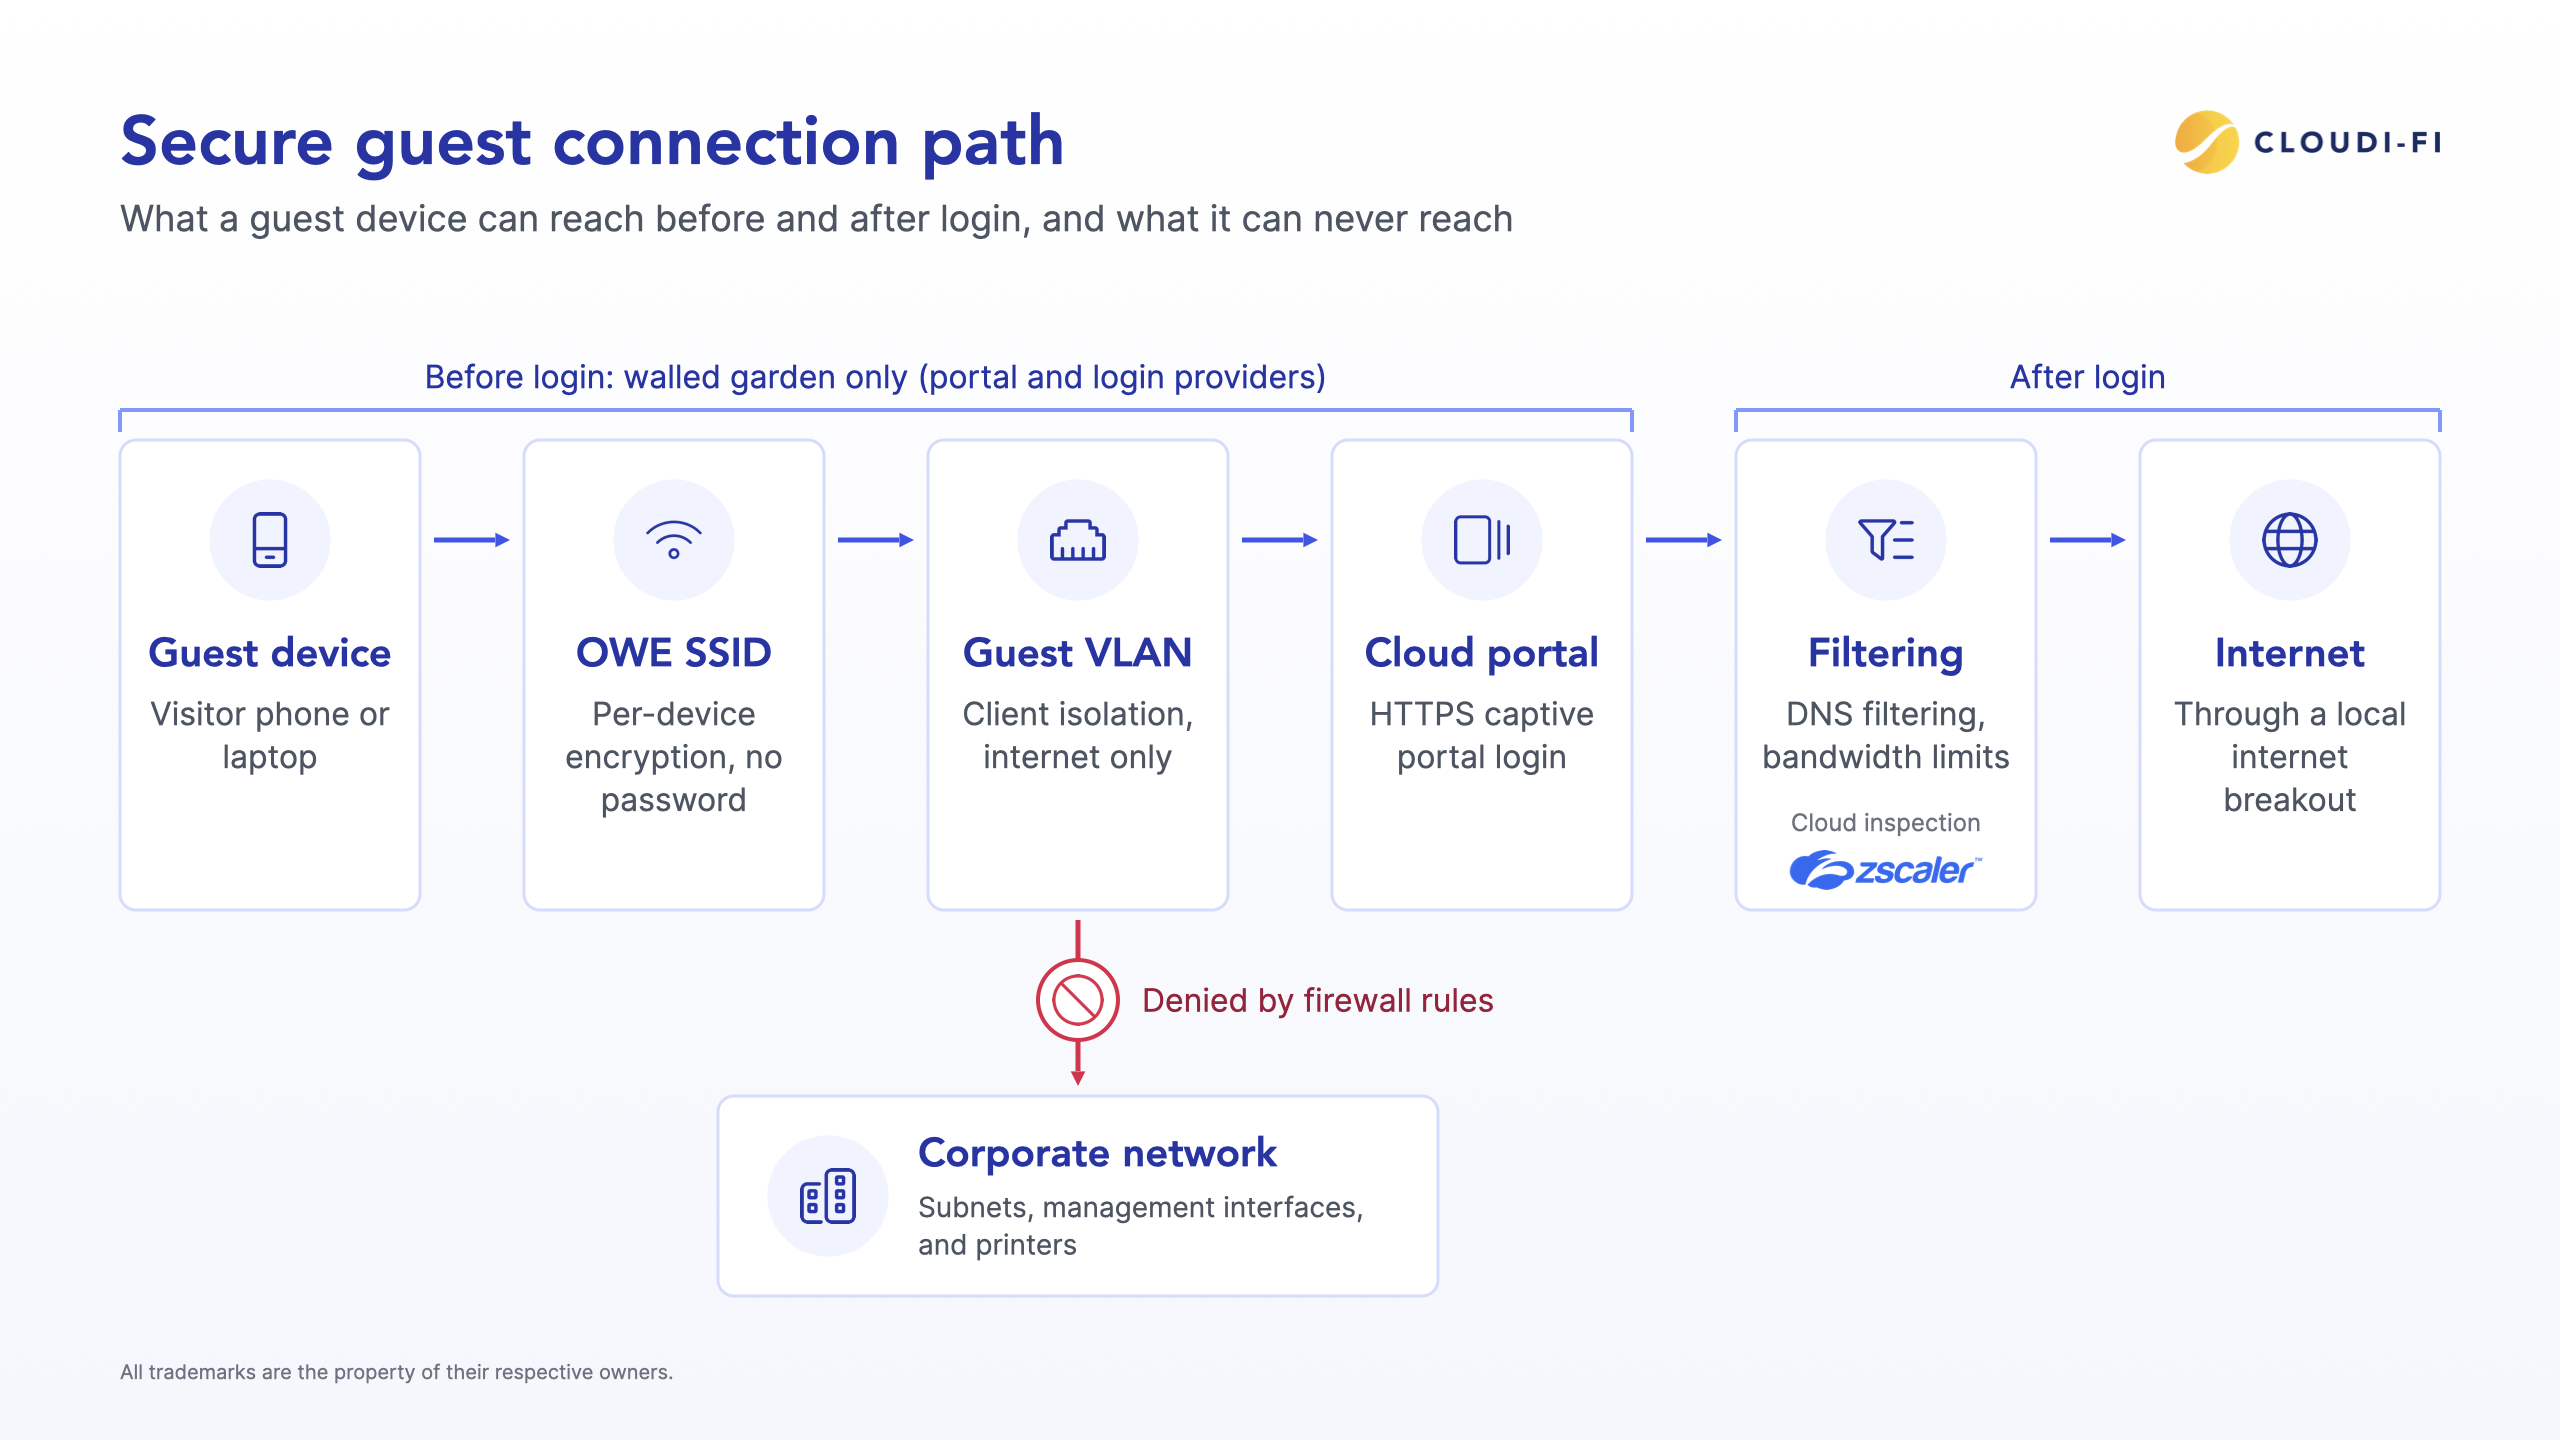
Put guests on a dedicated VLAN that can reach the internet and nothing else. Add firewall rules that deny guest traffic toward corporate subnets, management interfaces, and printers. Turn on client isolation on the guest SSID, so one guest device cannot reach another.
Segmentation limits the damage if a guest device is infected or an attacker joins the network. It is also required where payment systems share a site, since standards such as PCI DSS expect guest networks to be separated from cardholder data. For device-level segmentation beyond guests, see how IoT network segmentation sets boundaries.
2. Serve the portal over HTTPS only
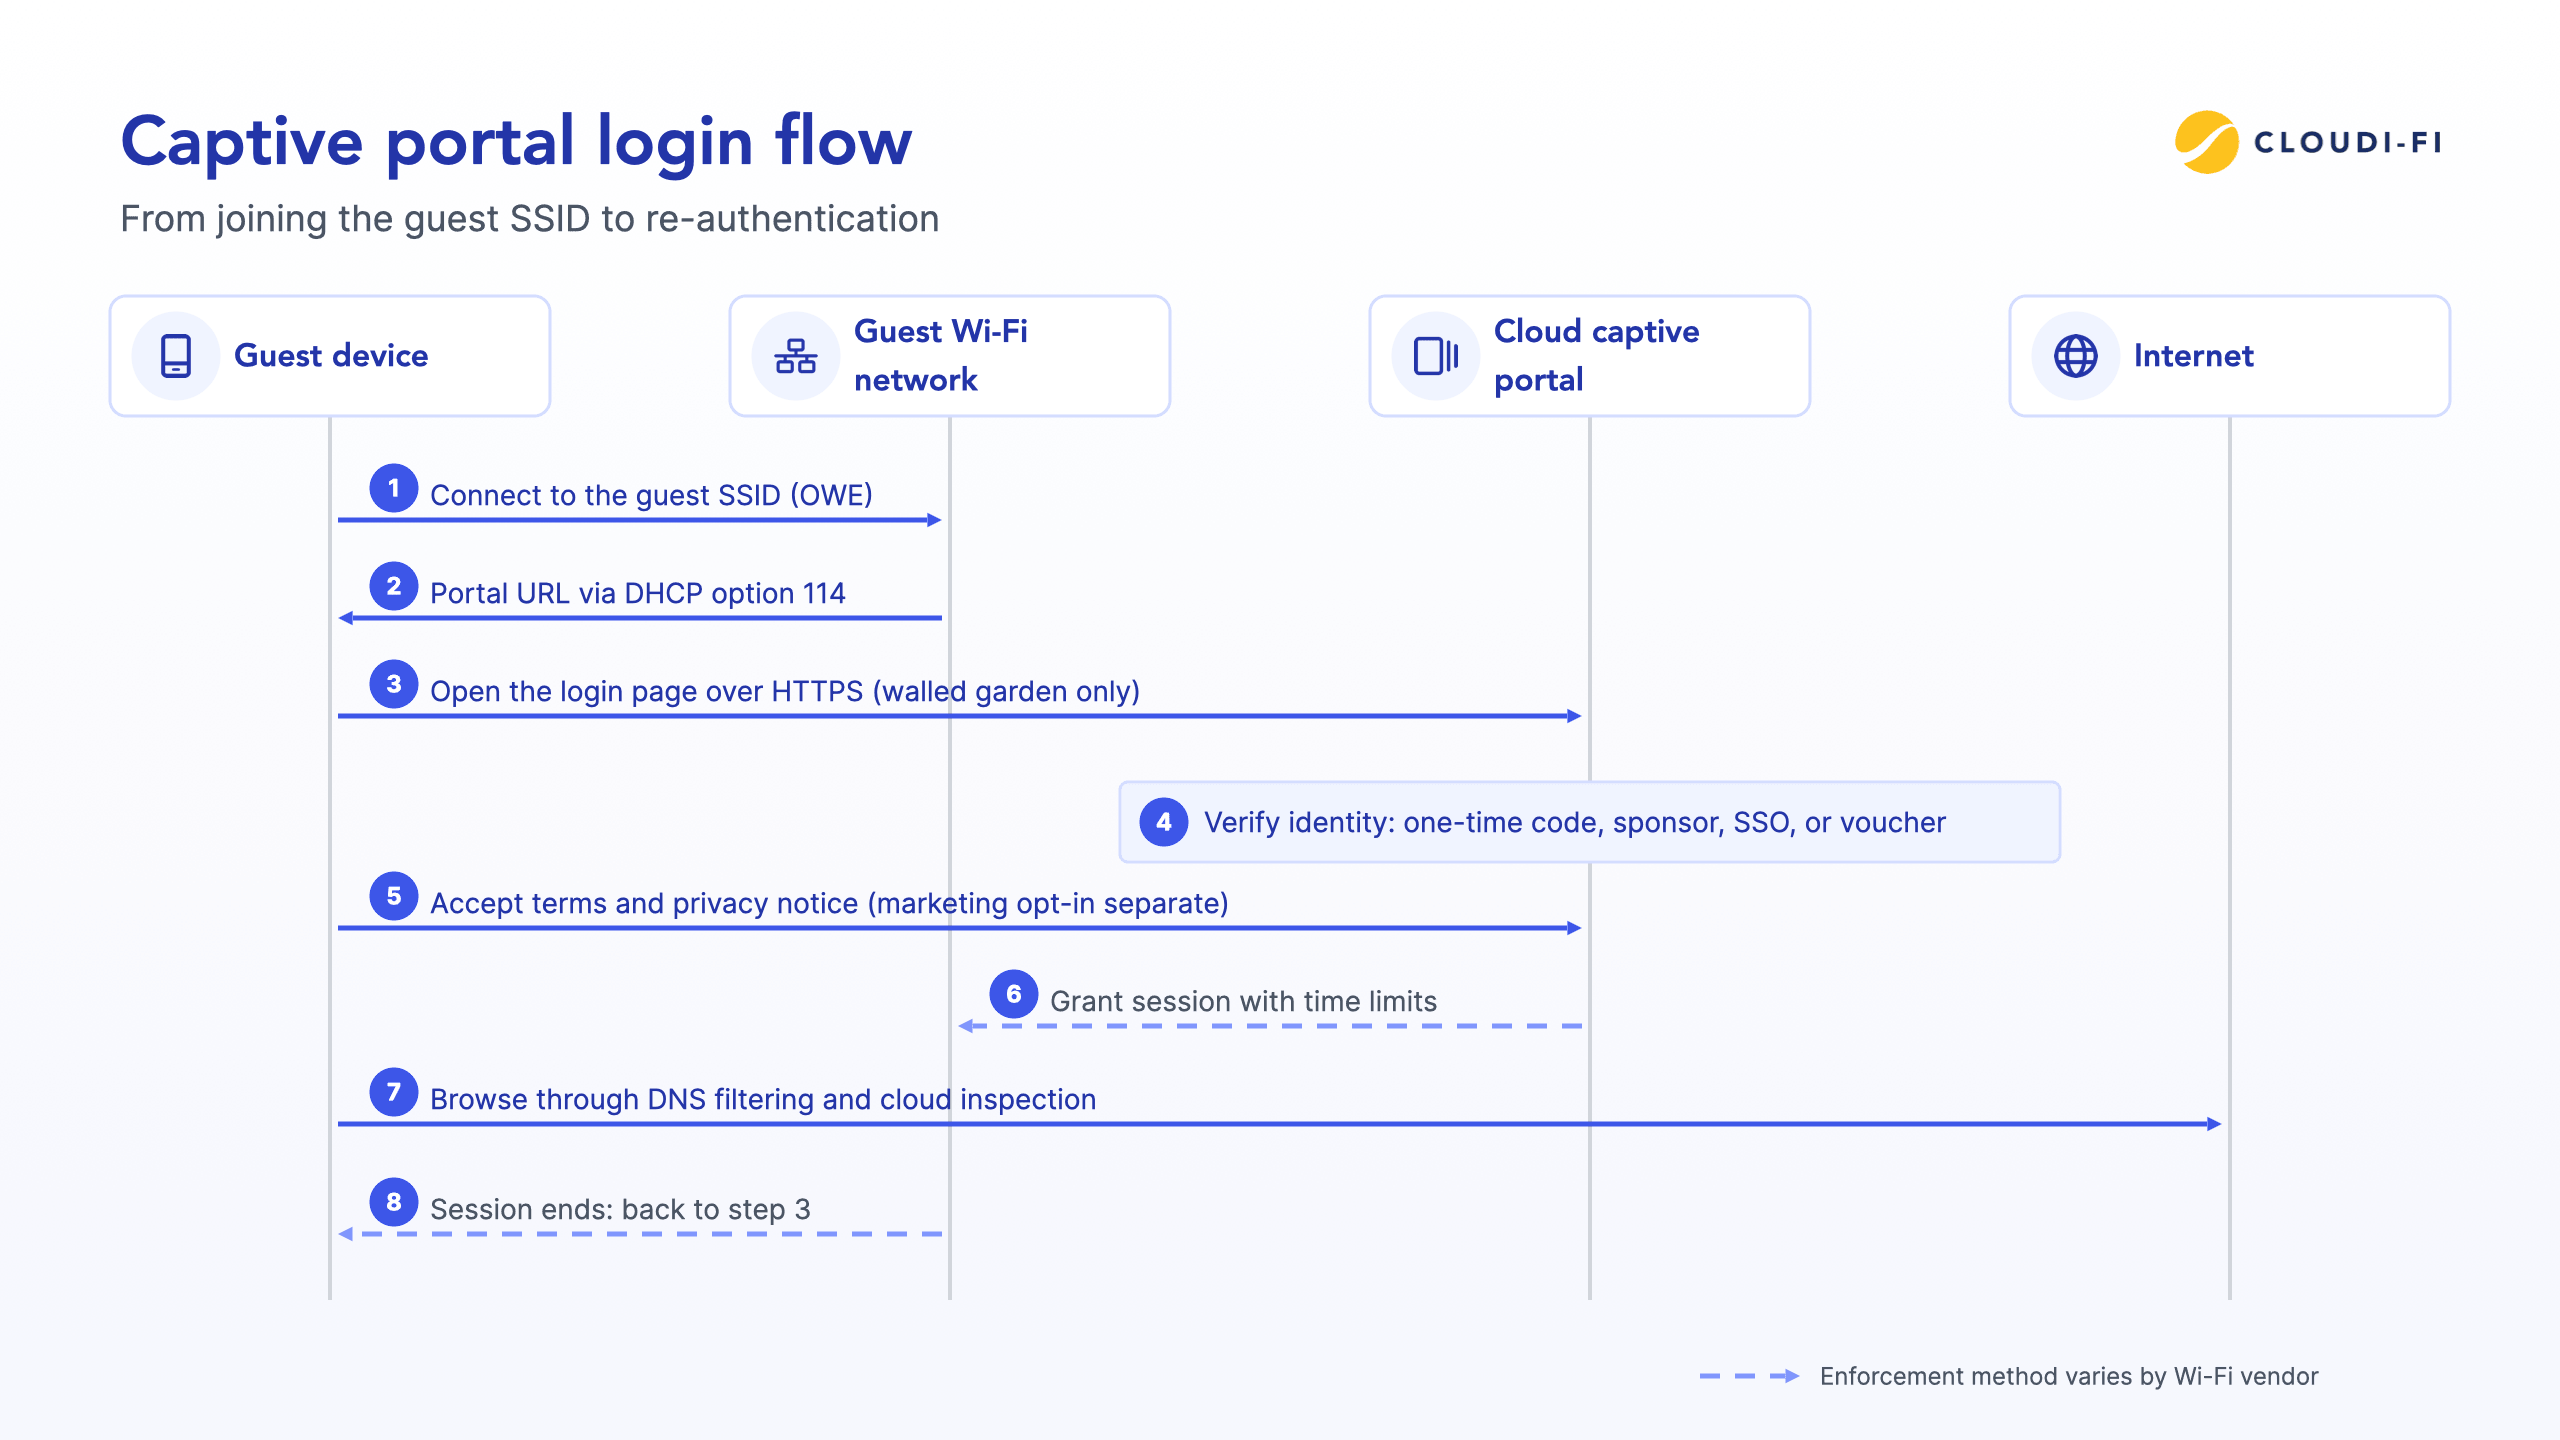
The login page collects names, emails, phone numbers, and one-time codes. Serve it only over HTTPS with a valid, publicly trusted certificate, and never fall back to plain HTTP. Configure the redirection so guests are not shown browser certificate warnings, which train users to click through real attacks. Cloudi-Fi documents this for Fortinet equipment in how to enable HTTPS redirection without browser warnings.
Also advertise the portal through the Captive Portal API (DHCP option 114). Devices then find the login page directly instead of relying on a hijacked web request, which makes detection more reliable on iOS. See captive portal identification with DHCP option 114.
3. Encrypt the open SSID with OWE
A traditional open SSID sends every guest's traffic over the air unencrypted. Opportunistic Wireless Encryption (OWE), marketed as Wi-Fi Certified Enhanced Open, gives each device its own encryption keys with no password to share. The captive portal still handles identity and terms acceptance on top.
Use OWE transition mode during migration. It pairs an open SSID with an OWE SSID, so devices that support OWE connect encrypted while older devices still connect.
4. Use identity-based login methods
Choose a login method that ties each session to a real identity:
- SMS or email one-time codes for visitors.
- Sponsor approval, where an employee approves a guest's access.
- Single sign-on (SSO) with your identity provider for employees and contractors using personal devices.
- Vouchers or access codes for events and short stays.
Rate-limit code requests and lock out repeated failures to stop brute-force attempts and SMS cost abuse. Social login is convenient for guests, but it shares data with a third party, so treat it as a user experience choice rather than a security control.
5. Keep the walled garden minimal
The walled garden lists the domains guests can reach before they log in, such as the portal itself and login providers. Every extra domain is a path around the portal. Allow only what authentication needs, review the list when you change login methods, and remove entries you no longer use. See how to set up a walled garden for your captive portal.
6. Control session length and re-authentication
Set a session lifetime and an idle timeout that match how long guests actually stay, for example a workday for office visitors. Require re-authentication when a session expires. Shorter sessions reduce the window in which an unattended or stolen device stays connected.
Do not rely on the MAC address alone to recognize returning devices. Current iOS, Android, and Windows versions can use a private or rotating MAC address per network, which breaks MAC-based session tracking and makes MAC allow lists unreliable.
7. Detect rogue portals and evil twin access points
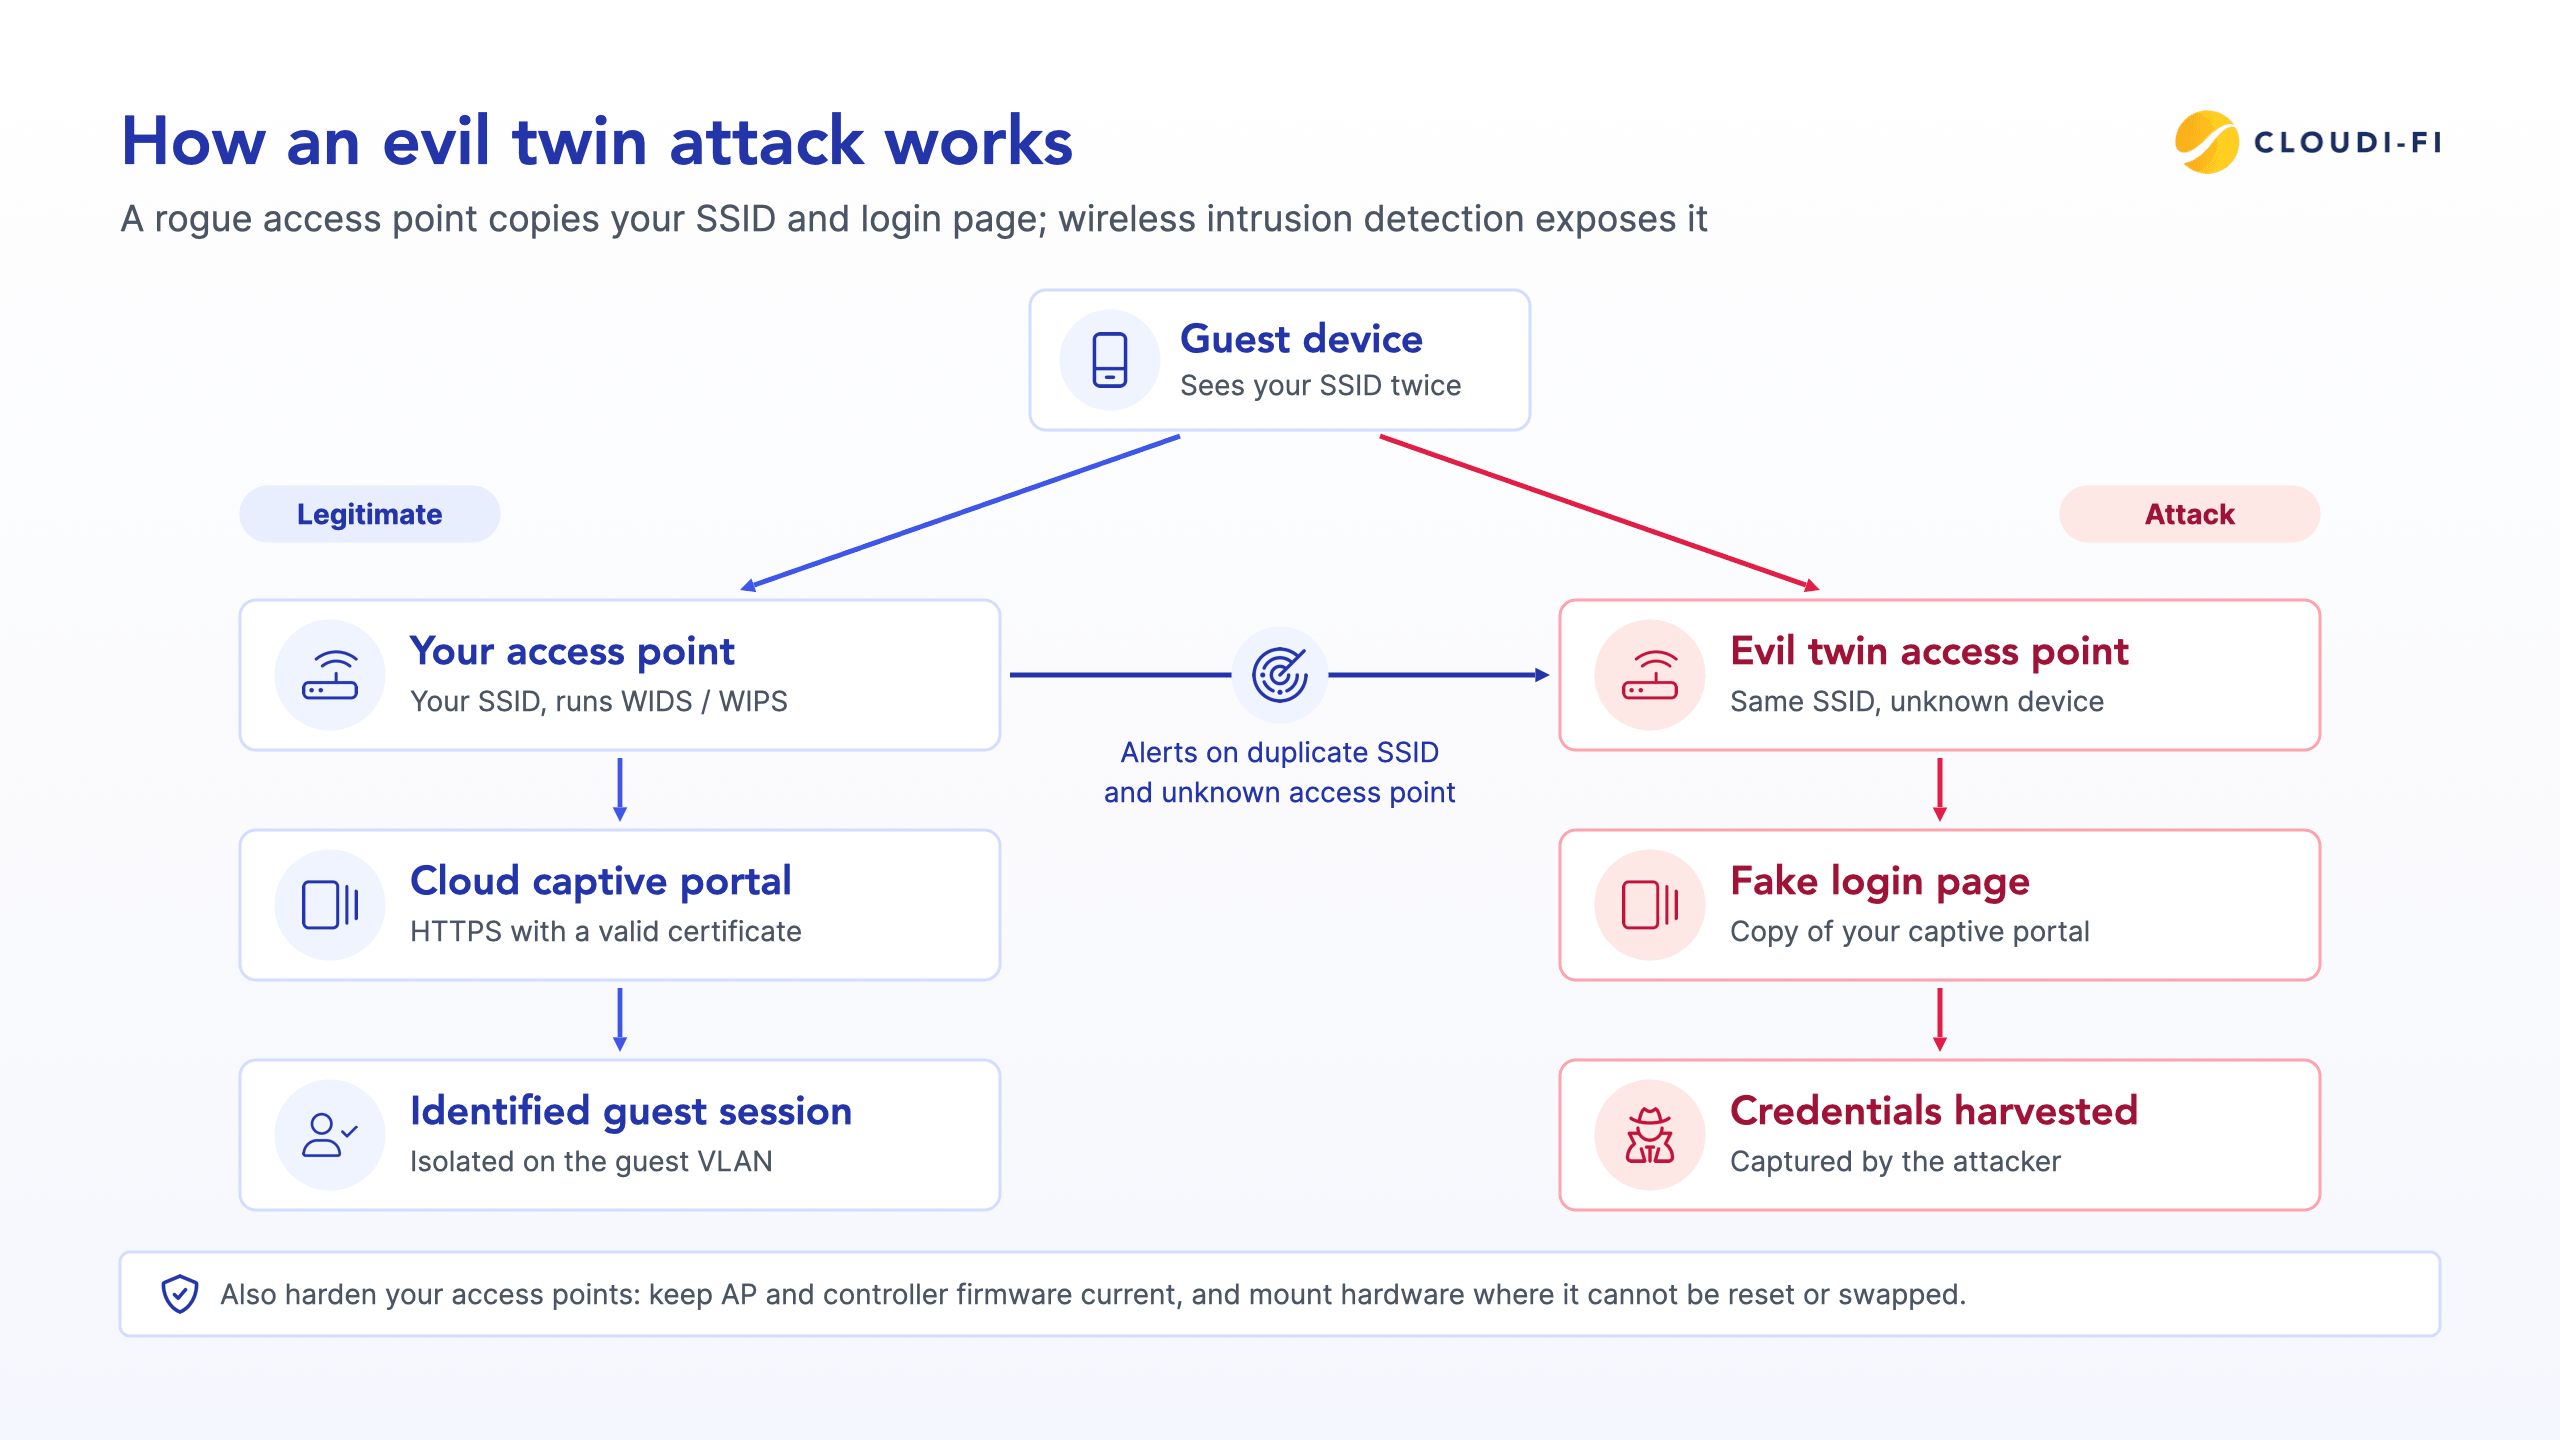
An evil twin is a fake access point broadcasting your SSID with a copy of your login page, built to harvest credentials. Use wireless intrusion detection (WIDS) or prevention (WIPS) on your access points to alert on duplicate SSIDs and unknown access points. Keep access point and controller firmware current, and mount hardware where it cannot be reset or swapped.
8. Filter and inspect guest traffic
Authentication decides who connects. Traffic controls decide what they can reach once online. Apply DNS filtering to block malware, phishing, and illegal content categories, as described in how to implement DNS filtering. For deeper inspection, send guest traffic to a cloud security platform such as Zscaler through a local internet breakout, instead of backhauling it to a data center.
Set bandwidth limits per user, so one guest cannot degrade the network for everyone.
9. Log connections and keep records as local law requires
Many countries require public Wi-Fi providers to keep connection records, such as who connected, when, and from which device, for a set period. Requirements differ by country, so map them for every country where you run guest Wi-Fi. Keep logs in a secure, access-controlled store, and feed them into your security monitoring. Learn more about the legal obligations of public Wi-Fi hotspots.
10. Collect consent and personal data lawfully
The portal is where you inform guests and collect consent. Show the terms of use and a privacy notice before access, make marketing consent a separate opt-in, and collect only the data you need. Privacy laws such as the GDPR in Europe and comparable laws in other regions set rules for consent, retention, and data subject requests. Configure the portal per country, since one global setting rarely meets every local rule. See how Cloudi-Fi supports global data privacy compliance.
How Cloudi-Fi applies these practices
Cloudi-Fi runs the captive portal as a cloud-based service on top of existing Wi-Fi infrastructure from vendors including Cisco Meraki, HPE Aruba Networking, Fortinet, and Juniper Mist. The portal is served over HTTPS from the cloud, so there is no portal server to patch on site. Guests authenticate through identity-based methods, and each user profile receives its own security policy. Guest traffic can break out locally to Zscaler for inspection, and portal settings adapt to the data privacy rules of each country where the organization operates.
Next step
These practices are easier to apply across many sites when the portal runs in the cloud. Explore Cloudi-Fi Captive Portal.
FAQ
Is it safe to log in to a captive portal?
It is generally safe on a legitimate network that serves its portal over HTTPS. Check for a valid HTTPS connection with no certificate warning, avoid entering passwords for other accounts, and use a VPN for sensitive work on networks you do not control.
What makes a captive portal secure?
A secure captive portal combines HTTPS login, guest isolation, identity-based authentication, and traffic controls after login. Read more about what a secure captive portal is.
Does OWE replace a captive portal?
No. OWE encrypts the wireless connection, while the captive portal identifies the guest and records consent. Used together, they give guests an encrypted connection and give you an identified session.
Can a captive portal work alongside 802.1X?
Yes. Most organizations use 802.1X for employees and managed devices, and a captive portal on a separate SSID for guests. See how 802.1X authentication works.
Why does my phone show a captive portal login page?
Your phone detected that the Wi-Fi network requires a sign-in before internet access, usually to accept terms or verify an identity. The login page opens automatically so you can complete that step.